Automated penetration testing that runs continuously in the background, without disrupting your environment.
Book a demoManaged Autonomous Pentesting is autonomous penetration testing that runs continuously and proves what an attacker could reach, across external and internal attack paths. Autonomous penetration testing is what we used to call automated pentesting.
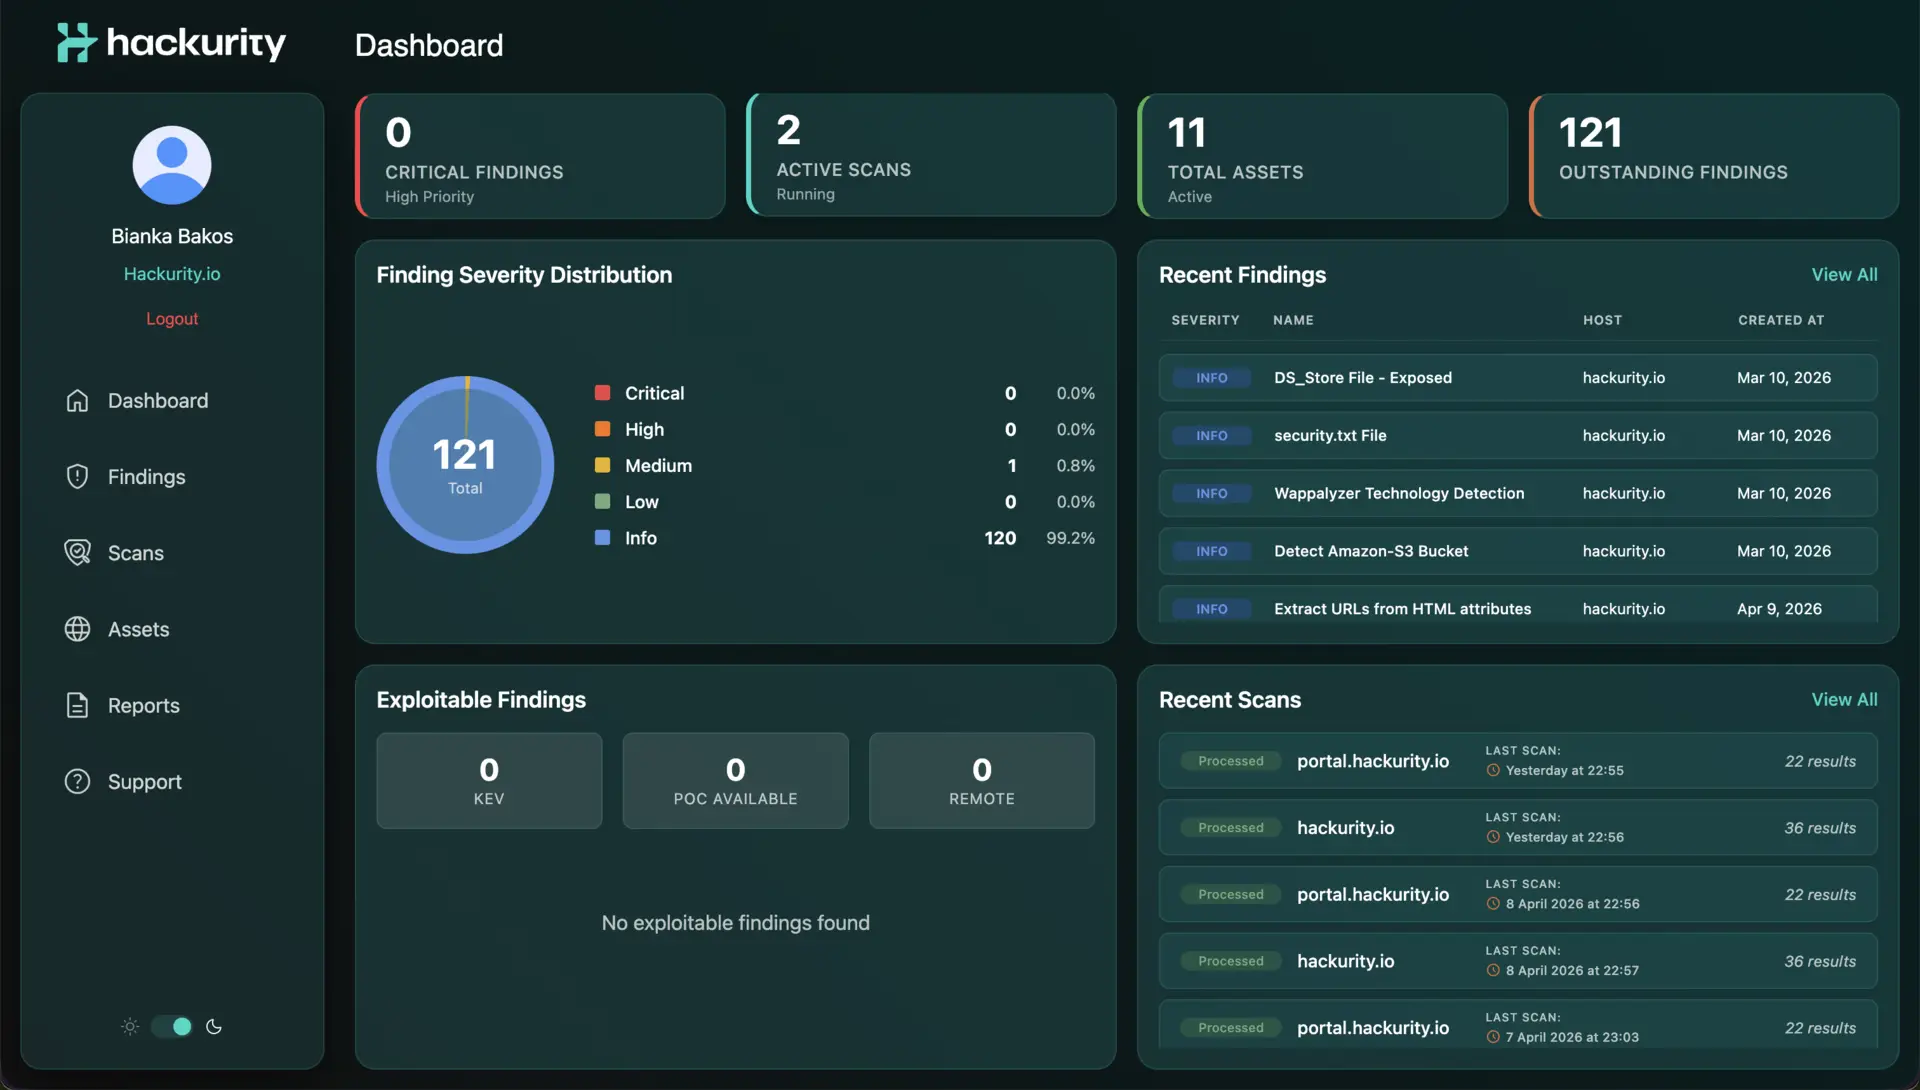
MAP proves which weaknesses an attacker could actually exploit, and how far they could get.
It safely simulates real-world attacks across your external IPs, web applications, APIs and endpoints. Instead of stopping at discovery, MAP chains findings together to validate real attack paths using payload-less exploitation. Each exploit is strictly constrained to the specific weakness being tested, so impact is proven without putting production systems at risk.
Testing re-scopes itself to every deployment, so a new release does not leave you with a scan that has gone stale. MAP uses AI to chain findings into attack paths, and our red team verifies every result before it reaches you.
Using the same architecture, MAP evaluates trust boundaries introduced through third-party software and updates, exposing how supply chain access could be abused in practice.
The result is a clear picture of how an attacker would move through your environment, what they would reach, and why it matters.
Download the product sheet (PDF)
Beyond Technology: The Human Factor in Cybersecurity Success
View Case StudyFrom Scanner Fatigue to Focused Remediation: CODE24 Optimises Its Security Operations
View Case StudyFrom Risk to Resilience: Hackurity Protects a Legacy in Real Estate Financing
View Case StudyRedmayne Bentley Strengthens Cybersecurity with Hackurity
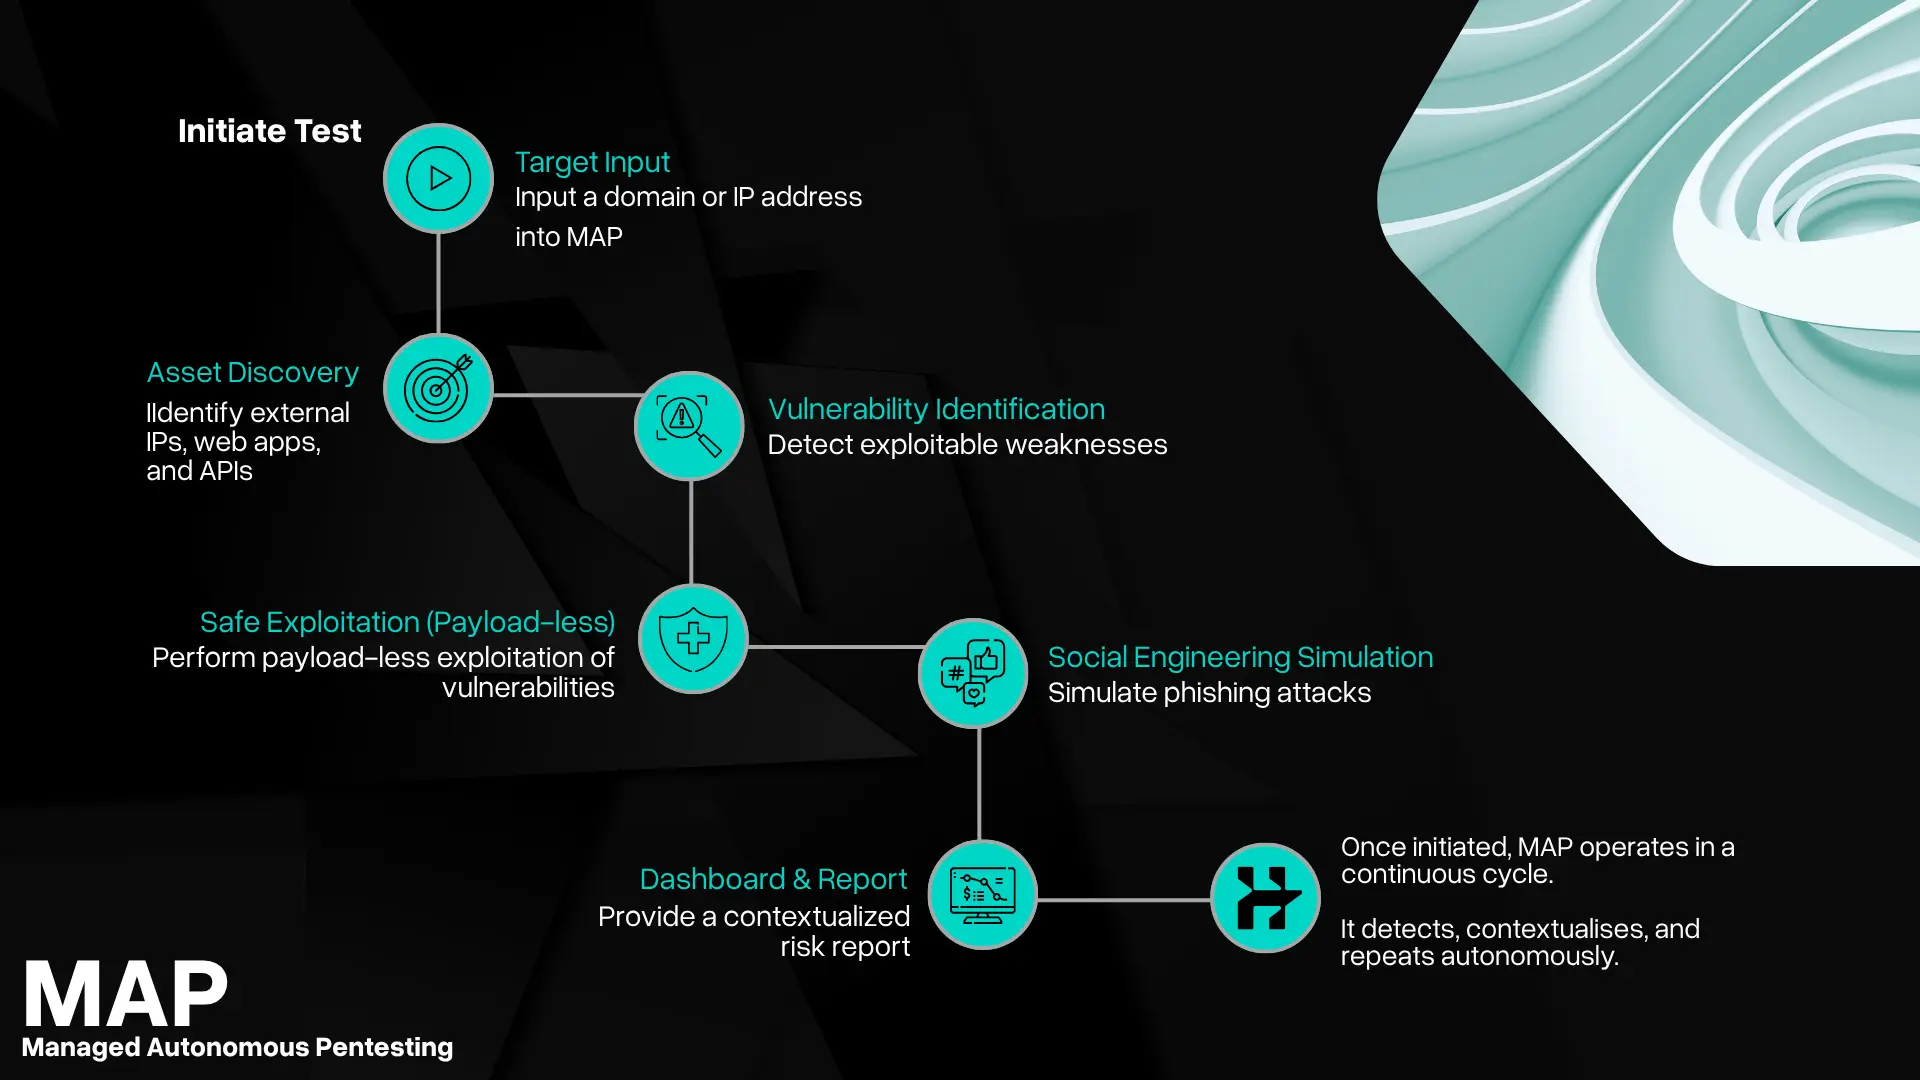
View Case StudyMAP follows six stages: target input, asset discovery, vulnerability identification, safe exploitation, post-exploitation and impact analysis, then a contextualised risk report.
You define scope by setting targets, which can be domains, IPs, applications, APIs or environments. We discover live assets, services and relationships, identify and validate exploitable weaknesses, exploit them safely to establish real impact, then map attack paths and escalate privileges to measure what an attacker could actually reach.
Payload-less exploitation proves a weakness is exploitable without deploying the malicious code a real attacker would use. Each exploit is strictly constrained to the specific weakness being tested.
This is how impact is demonstrated without putting production systems at risk. You get proof that an attack path works, and nothing is installed, altered or left behind.
Yes. Testing is payload-less and every exploit is constrained to the specific weakness being tested, so impact is proven without disrupting operations.
All testing runs within controlled parameters agreed with you. We run real attack chains, including privilege escalation and access to business systems, but the outcome is a confidential report rather than a breach.
Yes. Internal testing works by deploying a Hackurity agent inside your network, which creates a secure connection back to our platform.
External testing needs no installation at all.
Experience the power of Hackurity with a personalized Proof of Concept demonstration. See our solutions in action against your specific targets.
Book a demo